

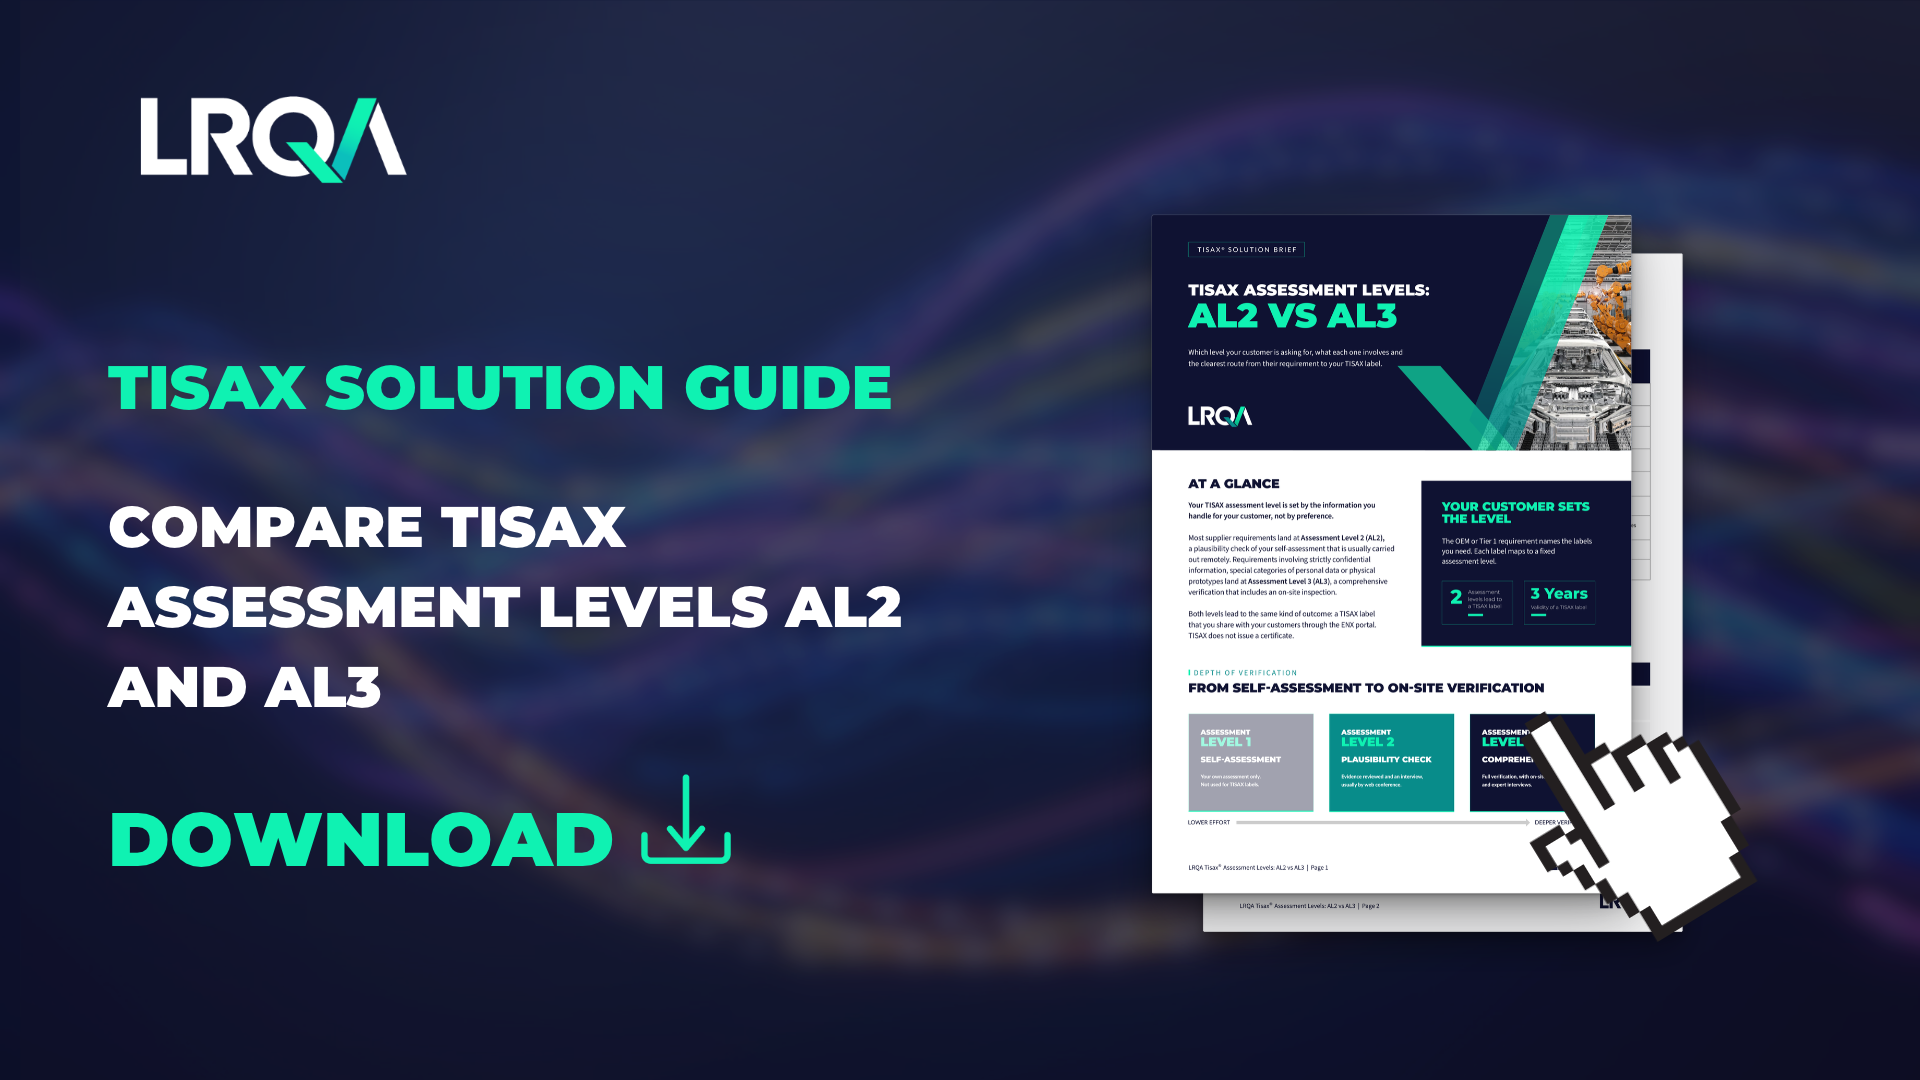
TISAX assessment levels: AL2 vs AL3
Free Solution Brief
Your customer sets your TISAX assessment level, not you. Each label in their requirement maps to a fixed level, and that level decides how closely your information security is checked. This guide compares AL2 and AL3 side by side and sets out the route from your customer’s requirement to your TISAX label.
Inside, you will find:
- What AL2 and AL3 involve, from a plausibility check that is usually done remotely to a full verification on site
- Which labels map to which level, including prototype protection
- Three checks to make before you register
- The five stages from requirement to label
- Three starting points, whether you hold ISO 27001, are building an ISMS or have not started
- Frequently asked questions
Download the guide to confirm what your customer is asking for before you register.
Latest news, insights and upcoming events
-
When the freezer becomes the attack surface: Retail OT...
Article
Europe's recent refrigeration cyberattacks show how exposed OT systems can disrupt food retail operations. Explore the risks, business...
Read more -
European supermarket cyber-attacks expose OT and supply chain risks
Article
Recent cyber-attacks targeting supermarket refrigeration systems across Europe highlight the growing risks connected operational technology poses to product...
Read more -
Forecasting the next PHP2Shell
Article
A forecast of the next internet-scale vulnerability and how organisations can prepare for classes of vulnerabilities rather than...
Read more -
PHP2Shell: What GRC leaders must learn from the crisis
Article
Discover what PHP2Shell reveals about cyber governance, vulnerability management, operational resilience and AI-driven cyber risk.
Read more -
What ISO 42001 does and does not get you...

Article
An obligation-by-obligation guide to ISO 42001 and the EU AI Act: what certification covers, what remains outstanding and...
Read more -
Global AI regulation and ISO 42001 explained

Article
Rules differ by market, but the governance they demand does not. See how one ISO 42001 management system...
Read more -
LRQA among first five NCSC assured CyAS providers
News
LRQA has been named one of only five NCSC Assured Providers under the new Cyber Adversary Simulation (CyAS)...
Read more -
Critical PHP Vulnerabilities Under Attack
News
Critical PHP vulnerabilities CVE-2026-109618 and CVE-2026-109619 are being actively exploited. Explore the risks, AI's role and steps to...
Read more -
Webinar: 2026 Rewind, 2027 Ready: Cyber, AI & Resilience
Event
Join LRQA's experts on 3 December to explore key cyber security, AI and resilience trends from 2026 and...
Register for webinar