

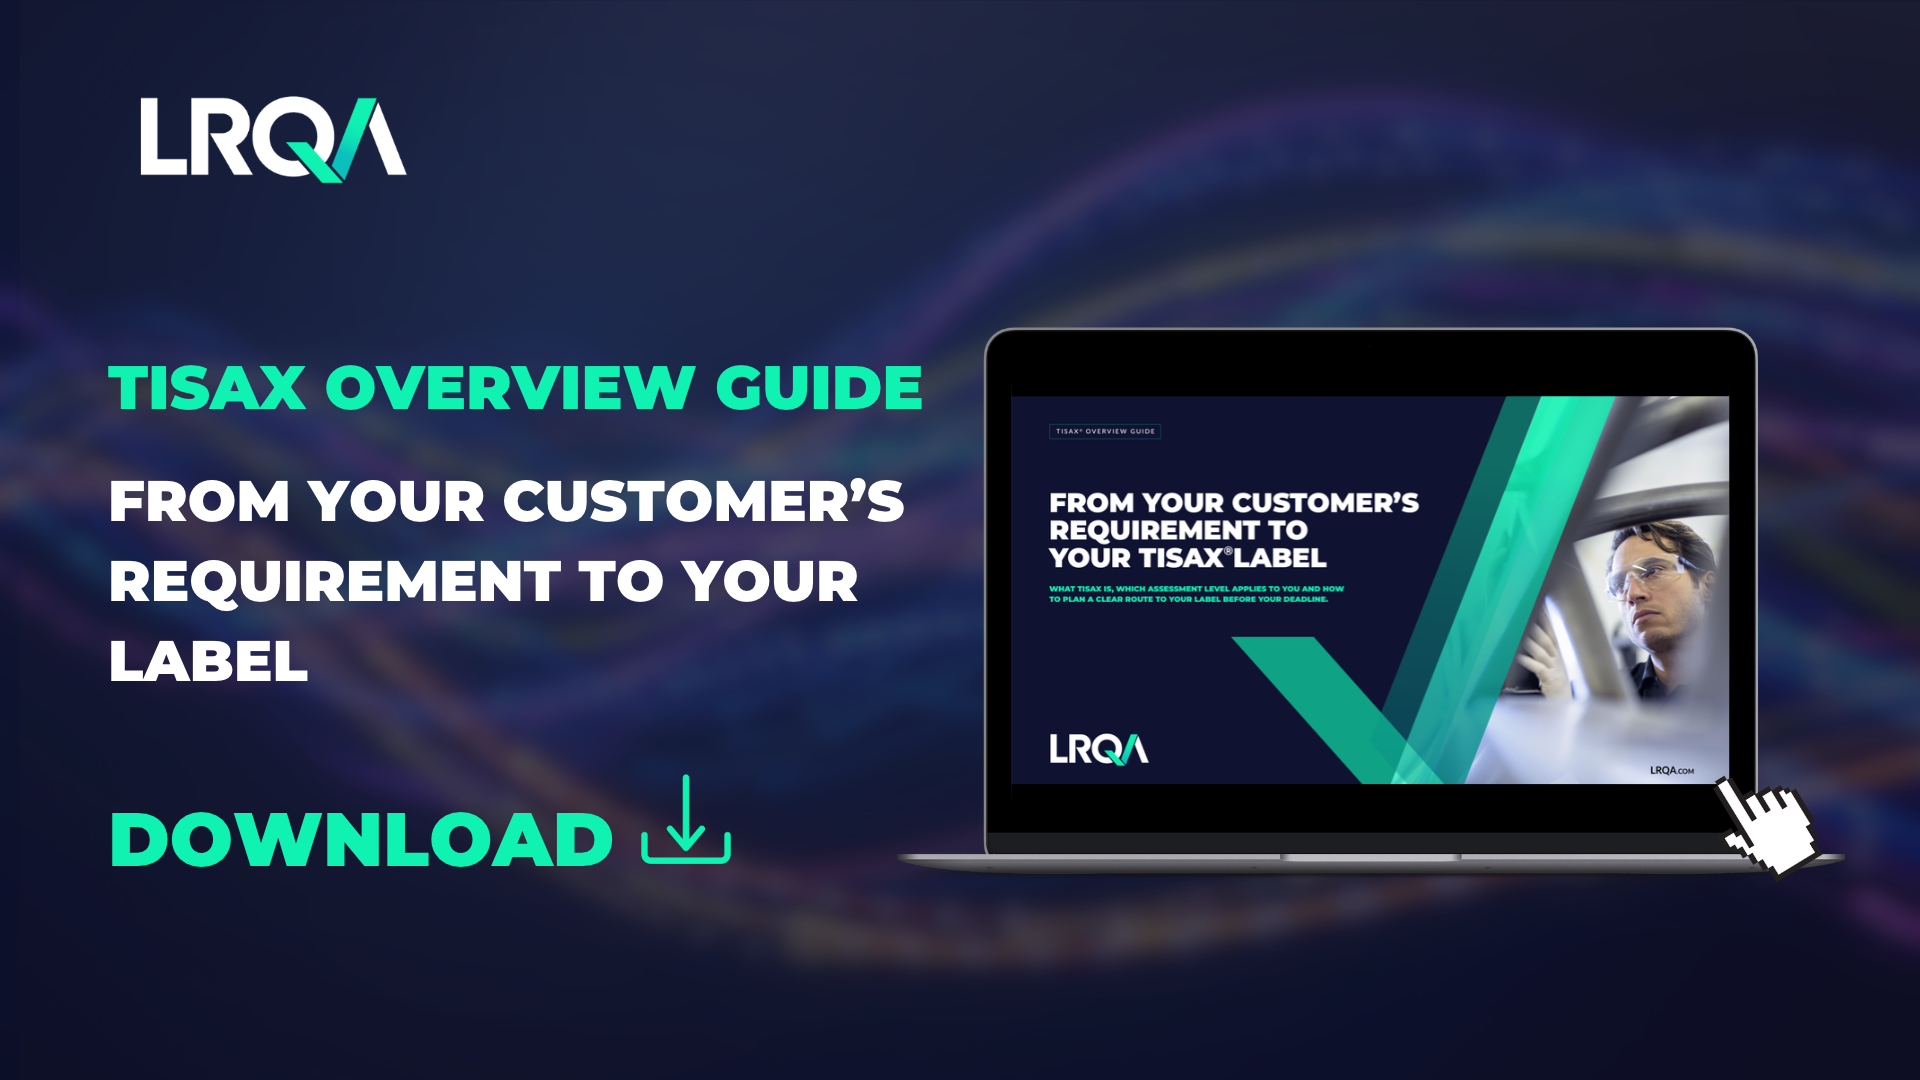
TISAX overview guide: from your customer’s requirement to your label
Free guide
Your OEM or Tier 1 customer has asked for a TISAX label. Their request names an assessment level, a scope and a deadline. This guide explains what each of those means and sets out the route from your customer’s requirement to your label.
Inside, you will find:
- What TISAX is and why it results in a label, not a certificate
- How to confirm the assessment level your customer requires (AL2 or AL3)
- Which labels apply to the information you handle
- The five stages from requirement to label
- Where you start, whether you hold ISO 27001, are building your information security management system or are starting from scratch
- What affects how long the process takes
- How LRQA supports you, with gap analysis and assessment kept as separate services
Download the guide to plan your route to TISAX with confidence.
Latest news, insights and upcoming events
-
What ISO 42001 does and does not get you...

Article
An obligation-by-obligation guide to ISO 42001 and the EU AI Act: what certification covers, what remains outstanding and...
Read more -
Global AI regulation and ISO 42001 explained

Article
Rules differ by market, but the governance they demand does not. See how one ISO 42001 management system...
Read more -
In machines we trust?
Article
LRQA CEO Ian Spaulding explores how independent assurance can build trust in AI, strengthen accountability and help organisations...
Read more -
OWASP AISVS 1.0: What CISOs Need to Know About...
Article
OWASP has released AISVS 1.0, a testable verification standard for AI systems. Discover what it means for your...
Read more -
ISO 22163 Explained: Why the rail industry is embracing...
Article
Discover why ISO 22163 is becoming the global standard for rail quality management and what it means for...
Read more -
Axios Supply Chain Attack: What happened and how to...
Article
Two compromised Axios npm versions installed a stealth RAT via a malicious dependency. Learn how the attack worked,...
Read more -
AI Penetration Testing for ISO 42001 Compliance
Article
ISO/IEC 42001 sets the framework for responsible AI management, but documentation alone does not prove your controls work....
Read more -
LRQA Wins Critical Infrastructure Protection Award 2026
News
LRQA wins Best in Critical Infrastructure Protection at the CybersecAsia Readers’ Choice Awards 2026, recognising its cybersecurity expertise...
Read more -
LRQA, Coval and Krew Pilot a New Standard for...
News
LRQA, Coval and Krew have piloted a new approach to AI assurance, combining independent governance assurance with real-world...
Read more